What Is Network Security? Types, Threats & Best Practices
Network security is the practice of protecting a network's infrastructure, traffic, and data from unauthorized access, misuse, and disruption. It works through layered hardware, software, and policies, including gateways, segmentation, access controls, and monitoring, that help protect business systems and maintain network availability.
For a small business or MSP, a single breach or unplanned outage can mean lost revenue, exposed customer data, and hours of downtime. This guide covers network security basics: how it works, the main types of protection, the threats they defend against, and the best practices businesses use to stay secure.
Key Takeaways
- Network security is a layered set of controls (hardware, software, and policies) that protects data confidentiality, integrity, and availability.
- It works through defense in depth: no single tool secures a network, so controls stack at the perimeter, within the network, and at endpoints.
- The main types include firewalls, access control, network segmentation, VPNs, intrusion detection and prevention, and wireless security.
- Common network security threats include malware, ransomware, phishing, unauthorized access, and risks from unsecured or unmanaged devices.
- Businesses and MSPs can build layered network security with business-grade infrastructure and consistent security practices, without the cost and complexity often associated with enterprise-scale deployments.
How Network Security Works
Network security exists to protect business networks and the data and systems that depend on them. Security professionals describe this goal through these three properties:
- Confidentiality: Restricting sensitive data to authorized users
- Integrity: Protecting data from unauthorized modification
- Availability: Keeping systems and data accessible when needed
No single tool delivers all three. Network security instead relies on defense in depth: layered controls at the perimeter, inside the network, and at the endpoint, so a failure in one layer doesn't expose the entire system. A firewall alone can't stop a compromised laptop from spreading malware to devices on the same VLAN. A strong password policy alone can't stop an unpatched device from being exploited.
In practice, this means coordinating several pieces of infrastructure. A gateway provides perimeter defense and encrypted remote access, while managed switches and VLANs separate traffic by function, placing guest Wi-Fi, point-of-sale systems, and file servers on separate network segments.
Access control policies then determine which users and devices can reach specific resources within and across those segments. Intrusion detection and prevention systems (IDS/IPS) and wireless security settings help detect or block threats that other controls don't stop. A centralized controller ties these pieces together into a single management interface.
Types of Network Security
Network security is best understood as a set of distinct but complementary controls, each addressing a different point where a network is vulnerable. The network security devices, technologies, and practices below cover several of the core controls used to protect business networks, from perimeter defense down to individual wireless connections.
Firewalls
A firewall controls inbound and outbound traffic according to defined security rules, allowing or blocking traffic based on criteria such as source, destination, port, and protocol. Firewalls are commonly deployed at the network perimeter, but can also control traffic between internal network segments.
Some gateways extend firewall capabilities with next-generation features like deep packet inspection (DPI), which analyzes traffic beyond basic packet headers to identify specific applications and traffic patterns. This lets administrators apply policies based on the applications passing through the network.
Select Omada gateways combine built-in firewall policies with DPI, access control lists (ACLs), and URL and keyword filtering, providing perimeter defense and application-level traffic visibility in a single device.
Access Control
Access control ensures only authorized users and devices can reach specific network resources. It combines authentication (verifying identity), authorization (determining what an authenticated user or device can access), and policies that enforce those decisions.
A least-privilege approach, where users and devices only get access to what they need, limits the damage of a compromised account or device. ACLs enforce this by defining which traffic is permitted or denied between networks, segments, or devices. VLAN segmentation can further limit the network resources a compromised device can directly reach when combined with appropriate access controls.
Network Segmentation (VLANs)
Network segmentation divides a network into isolated sections, limiting which devices and systems can communicate with one another. For a retail business, that might mean separating guest Wi-Fi from point-of-sale traffic so a compromised guest device can't directly access payment systems.
VLANs provide network segmentation, but they don't inherently prevent communication between VLANs once routing is enabled between them, often called inter-VLAN routing. Administrators can use ACLs and firewall policies to restrict or block inter-VLAN traffic and enforce the desired level of isolation.
A single managed switch and gateway can support multiple VLANs without requiring separate physical networks, with each VLAN typically associated with its own IP network and access policies. For a step-by-step walkthrough, see how to configure VLANs with Omada.
VPNs and Secure Remote Access
A VPN creates an encrypted tunnel between two endpoints, protecting traffic as it travels across an untrusted network such as the public internet. For businesses, this typically means securing connections between remote workers and internal resources, or between branch offices and headquarters.
Many business gateways support multiple VPN technologies, including IPsec, OpenVPN, WireGuard, and L2TP/IPsec, which differ in their encryption and authentication mechanisms, client support, and deployment requirements. When a gateway terminates the VPN tunnel, devices behind it can access remote network resources through the tunnel without requiring individual VPN client software on each device.
Intrusion Detection and Prevention (IDS/IPS)
An IDS/IPS monitors network activity for suspicious behavior and known attack patterns, alerting administrators to detected threats and, when configured for prevention, attempting to block them.
Detection typically uses signature matching, anomaly detection, stateful protocol analysis, or a combination of these methods. Signature-based detection compares observed activity against signatures of known attacks, while anomaly-based detection flags deviations from expected network behavior. Some systems also use stateful protocol analysis to compare observed protocol activity against expected protocol behavior and identify deviations.
Wireless Security
Wireless networks introduce a different security challenge that wired networks don't have: devices within radio range can attempt to connect. WPA3, supported on select access points, is the latest generation of Wi-Fi security, providing stronger authentication and encryption than earlier standards.
Beyond encryption, guest network isolation separates guest traffic from internal resources, while client isolation can restrict unnecessary communication between connected devices. For businesses serving walk-in customers or visiting contractors, a properly isolated guest network provides a simple way to keep untrusted devices away from internal resources.
Common Network Security Threats
Small businesses and MSP clients face a recurring set of common threats, many of which can be reduced through appropriate security controls.
- Malware and ransomware: Malicious software that can damage systems, steal or encrypt data, disrupt operations, or provide unauthorized access to systems.
- Phishing and social engineering: Deceptive messages, impersonation, or other manipulation techniques that trick users into revealing credentials, transferring information, or taking actions that compromise security.
- Unauthorized access: Attackers gaining entry through weak credentials, misconfigured access controls, or exposed services.
- DDoS and availability attacks: Attacks that overwhelm network, server, or application resources, disrupting availability for legitimate users.
- Unsecured or unmanaged devices: Personal, IoT, or bring-your-own-device (BYOD) devices connecting to the network without consistent security controls, monitoring, or management.
The BYOD and unmanaged device category deserves particular attention because these devices may fall outside an organization's standard security controls. Separating these devices into dedicated VLANs and applying appropriate ACLs and firewall policies can limit their access to internal resources without blocking them outright.
Network Security Best Practices
An effective network security strategy combines multiple controls and applies them consistently. The following practices apply to many business network environments.
- Segment the network so guest, employee, IoT, and point-of-sale traffic are separated and access between segments is restricted.
- Enforce least-privilege access, giving users and devices only the permissions they need.
- Keep firmware and software patched across gateways, switches, access points, and other network-connected systems.
- Use strong authentication and require multi-factor authentication (MFA) where supported, particularly for administrative and remote access.
- Use VPNs for remote access rather than directly exposing internal resources to the internet.
- Monitor network activity centrally and maintain consistent security configurations across sites.
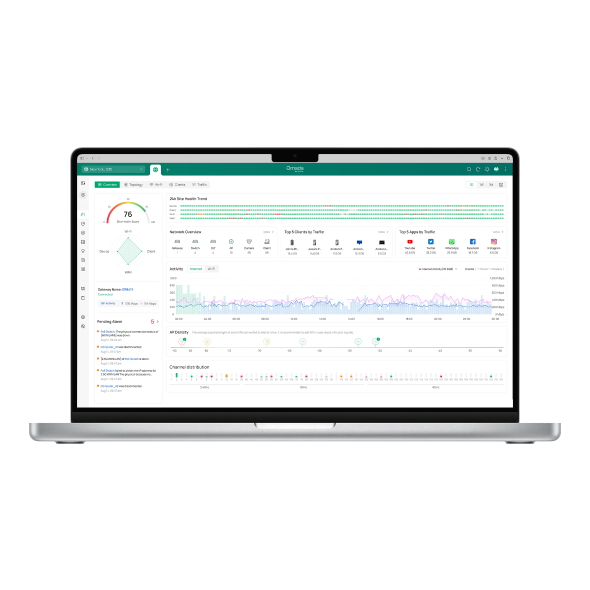
For a lean IT team or an MSP managing multiple sites, applying these practices individually across every device can become difficult to manage. An Omada software controller manages gateways, switches, and access points from a single interface, helping maintain consistent configurations and providing centralized visibility into network status, traffic, and events.
Network Security for Businesses and MSPs
Strong network security doesn't always require enterprise-scale complexity or budgets. A coordinated stack applies the same defense-in-depth principle larger organizations use, just at a scale a small IT team or MSP can manage. That stack typically includes a gateway providing firewall and VPN functions at the perimeter, managed switches providing VLAN segmentation, and a centralized controller tying it together.
A single-location business might deploy one gateway, a PoE switch, and several access points managed through a cloud controller. An MSP running that architecture across multiple client sites can use configuration templates and zero-touch provisioning to deploy consistent configurations without sending a technician to each site.
Planning Your Network Security Strategy
Network security isn't a single product; it's an ongoing, layered practice pairing the right infrastructure with consistent policies and monitoring. The types and best practices covered here give IT managers, MSPs, and system integrators a framework for evaluating where a network is exposed and what to prioritize first.
Building that defense starts with the right infrastructure: gateways, managed switches, and a centralized controller working together under a single management interface. Omada integrates gateways, managed switches, and access points into a single platform under centralized management. That gives businesses and MSPs a practical foundation for layered security without enterprise-level cost or complexity.
Frequently Asked Questions
What do you mean by network security?
Network security means protecting a network's infrastructure, traffic, and data from unauthorized access, misuse, and disruption. It combines hardware like gateways and switches, security technologies like firewalls, and policies like access control to keep the network available and protected.
What are the main types of network security?
The main types include firewalls, access control, network segmentation through VLANs, VPNs for encrypted remote access, intrusion detection and prevention systems, and wireless security such as WPA3. Most business networks combine several of these rather than relying on just one.
What is the difference between network security and cybersecurity?
Cybersecurity is the broader field covering protection of digital systems, including applications, endpoints, networks, and data. Network security is a subset of cybersecurity focused on protecting network infrastructure, communications, traffic, and connections between systems.
What are the most common network security threats?
Common threats include malware and ransomware, phishing, unauthorized access through weak credentials or misconfigured controls, DDoS attacks that disrupt availability, and unsecured or unmanaged devices connecting without consistent security policies.
How can a business improve its network security?
A business can improve network security by segmenting traffic with VLANs and restricting access between segments, and by enforcing least-privilege access. Other key steps include keeping firmware and software patched, requiring multi-factor authentication (MFA) where supported, using VPNs for remote access, and monitoring network activity centrally.
What is the best network security for a business?
There's no single "best" solution; effective network security combines multiple layers suited to the business's needs. For many small businesses and MSPs, a practical starting point is a firewall and VPN gateway paired with VLAN segmentation. Enforcing that segmentation with ACLs or firewall policies, plus adding centralized network management and monitoring, rounds out a solid baseline.